




Third-Party Risk Management
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management. 
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management.

A 2025 BlueVoyant survey found 97% of organizations were negatively impacted by a supply chain breach last year, up from 81% the year before, even after record spending on third-party risk programs. That gap between what companies are investing and what they're actually stopping is the real third-party cyber risk problem: visibility hasn't kept pace with how many vendors now touch your systems.
Granting a vendor access to your systems means their security posture becomes part of yours. When their defenses fail, the breach doesn't stay on their side of the relationship, it reaches your data, your customers, and your compliance obligations.
Third-party cyber risk is the security exposure your organization takes on when a vendor, contractor, or service provider with access to your systems or data has a security gap of their own. If a third party's defenses fail, the breach can reach your business even though the weakness was never inside your walls.
A well-designed third-party risk management (TPRM) program can help you monitor these vulnerabilities continuously, identify threats early, provide actionable insights, and reduce exposure from unchecked third-party risk intelligence gaps.
With the increasing dependence of businesses on outsourcing more work, third-party risk is a critical concern. Breaches originating in partner networks are also common. For instance, According to the Verizon 2026 Data Breach Investigations Report, 48% of breaches now involve a third party, up 60% year-over-year, making third-party exposure one of the fastest-growing categories of breach risk rather than a static one, making proactive tools for cybersecurity risk assessments essential to stay ahead of these vulnerabilities.
The takeaway? If one of your trusted partners gets hit, your business could feel the impact just as bad, if not worse. Without adequate third-party cyber assessment and monitoring, these inherent risks can quickly escalate and lead to serious consequences like regulatory fines, financial losses, lawsuits, and even lasting reputational damage..
Across industries, organizations have suffered massive data breaches, financial losses, and reputational damage due to vulnerabilities introduced by external vendors.
In the month of May 2023, the Clop ransomware gang exploited a zero-day in a flaw found in the MOVEit file-transfer system used by a vendor for the U.S. Centers for Medicare & Medicaid Services (CMS). Almost 946,801 beneficiary records (names, Social Security numbers, claim info) for Wisconsin were compromised, demonstrating how flaws in vendor software can promptly escalate into major financial-sector catastrophes.
On February 21, 2024, a cyberattack hit Change Healthcare, a critical third-party provider in the U.S. healthcare system. This disrupted payouts forced patients to pay out-of-pocket, and halted claims processing across major providers like UnitedHealth, CVS, and Walgreens leading to an estimated $100 million per day in losses.
On June 19, 2024, CDK Global (a major IT provider for car dealerships) was hit by a ransomware attack through a third-party vendor. The breach disrupted thousands of dealerships across North America, prompted a $25 million ransom payment, and was followed by multiple lawsuits.
Similarly, In April 2025, Scattered Spider hackers leveraged compromised credentials at Tata Consultancy Services (TCS), a key third-party vendor, to infiltrate Marks & Spencer. The attack caused widespread outages, customer data exposure, and an estimated £300 million loss.
These incidents underscore the reality that even the most trusted partners can become gateways for cybercriminals. Whether through software flaws, credential theft, or ransomware-laced access points, third-party risks can trigger widespread fallout.
It is not just software providers or IT vendors that you need to worry about. Even non-technical vendors like photocopy technicians can pose a threat if they access sensitive areas or connect to your internal systems. Something as simple as walking through a data room or plugging into your network can create a potential backdoor for cyber threats.
That’s why it’s essential to monitor all vendor interactions closely. Using platforms that offer third-party risk intelligence can help spot early warning signs before such minor oversights turn into full-blown breaches.
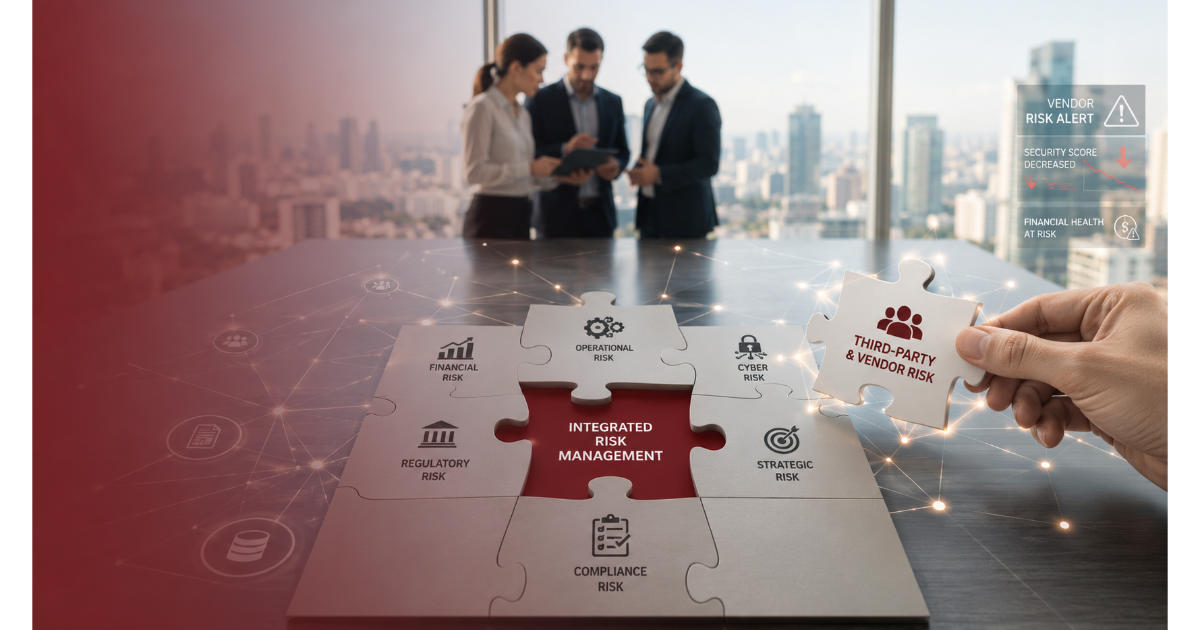
Third parties can introduce six distinct categories of risk, and they rarely stay contained to just one:

| Risk Type | What It Means | Example |
| Cybersecurity | A vendor's security gap becomes your exposure, through malware spread or an unpatched flaw attackers can reach through | An unpatched vendor server lets attackers pivot into your network |
| Operational | A critical supplier fails to deliver, or delivers below the committed service level, disrupting your operations | A key supplier's outage halts your production or service delivery |
| Legal and Compliance | A vendor's non-compliance or data mishandling exposes you to fines or penalties under regulations like GDPR or HIPAA | A vendor's mishandled customer data triggers a regulatory fine on your business |
| Reputational | A vendor's failure, especially a breach, damages your public trust even when you weren't directly at fault | A partner's data breach generates negative press about your company |
| Financial | Direct monetary loss from lost sales, or the cost of fixing problems a vendor caused | Unbudgeted remediation costs after a vendor-caused outage |
| Strategic | A vendor's failure derails a business objective you were depending on them for | A product launch stalls because a dependent vendor couldn't deliver on time |
These categories rarely stay isolated. A single cybersecurity breach can trigger legal fines, financial losses, and reputational damage at the same time, which is why mature TPRM programs treat these six risks as connected, not separate checkboxes.
Every industry faces unique third-party risks, but the need for prompt management is universal. Here's how various sectors approach it in practice:
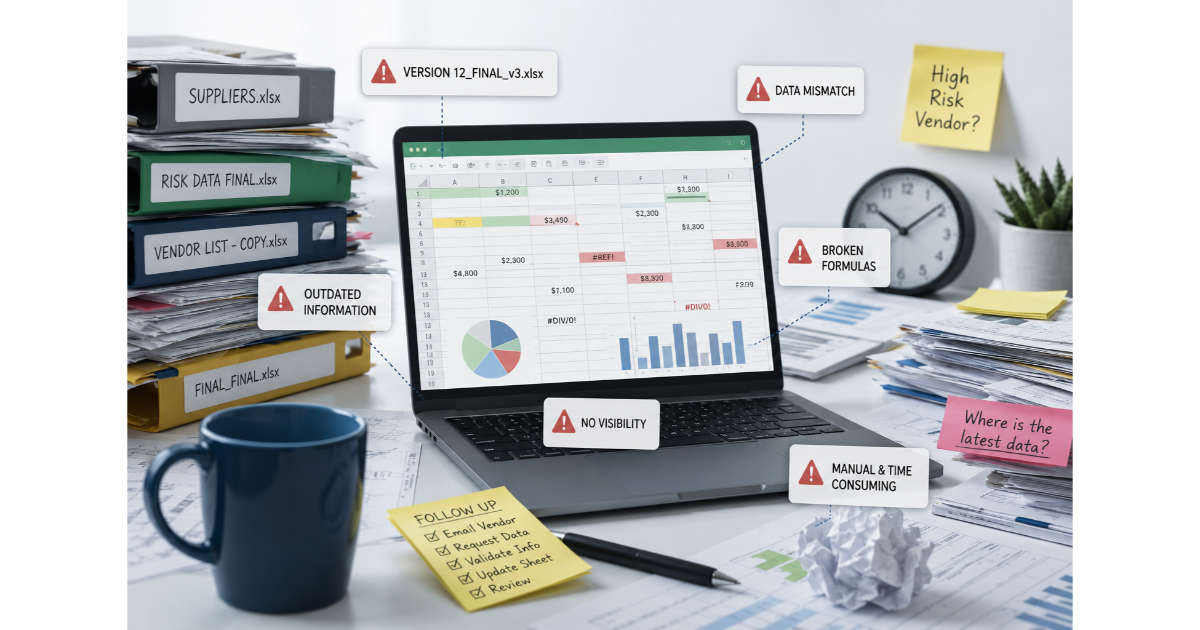
Before we talk solutions, it is crucial to understand the daily roadblocks most businesses face while managing third-party risk manually:

Emerging threats often go undetected until it's too late. These are exactly the kinds of inefficiencies that third-party risk management platforms like ComplyScore® eliminate by centralizing vendor data, automating tasks, and providing actionable insights from one place.
Reducing third-party cyber risk requires a structured program and timely third-party risk assessments. A 2025 BlueVoyant survey found 97% of organizations reported negative impacts from a supply chain breach in the past twelve months, up from 81% the year before, underscoring that despite rising TPRM budgets, breach exposure keeps climbing rather than leveling off
This means most organizations do not have complete visibility into their third-party relationships and potential vulnerabilities, highlighting a huge blindspot in most high-risk programs. You can implement these three basic steps to get started:
You can’t manage risk if your security teams don't know your vendors. Begin by listing every third-party provider that has access to your systems. This inventory should have primary vendors as well as their subcontractors. Regularly update the list to add new contractors and remove old ones. Automate this process to save a lot of time and manpower. Some organizations use attack surface management tools like Microsoft Defender to discover every new external connection or IP that interacts with their network. A clean, updated inventory ensures you know who has access to what and can monitor it promptly.
With your inventory in hand, implement a formal way to evaluate vendors. Send security and compliance questionnaires and guidelines to any new or existing vendor and review their responses against your requirements. You can tailor the assessment to the vendor’s role. For example, a cloud storage provider handling sensitive data will need a more thorough audit than a stationery supplier. The goal is to gather key risk and compliance information about each vendor’s practices. This step helps you decide which partners meet your standards and identifies gaps that need remedy.
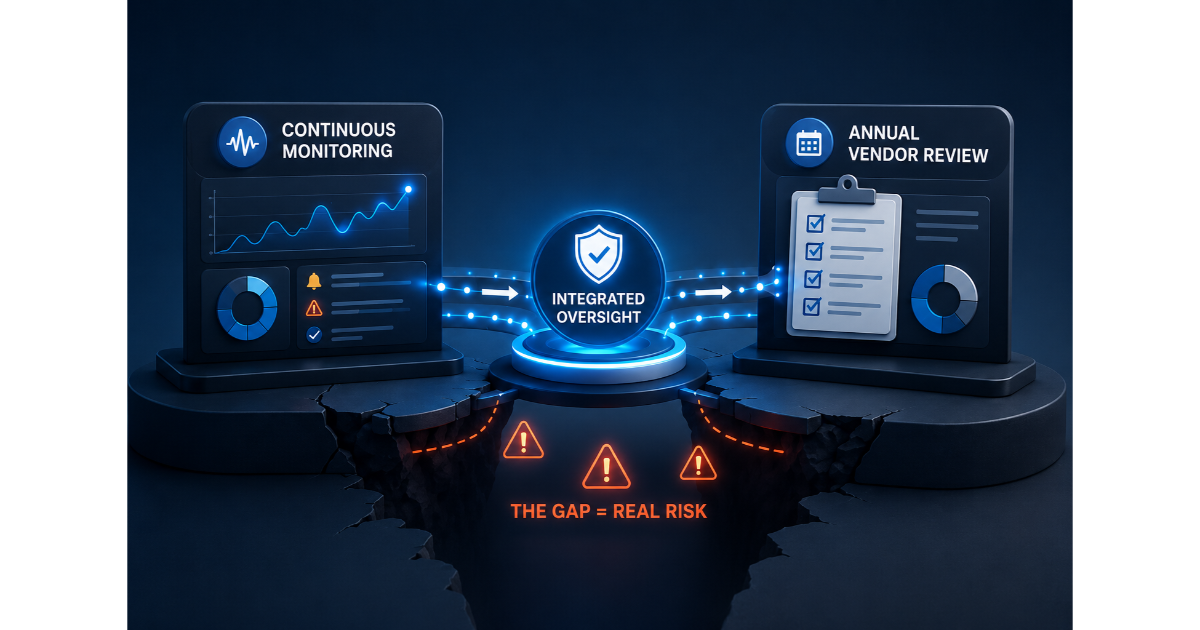
Once you have processes for inventory and assessment, incorporate them into an ongoing TPRM framework. Categorize vendors by risk level such as high, medium, and low, and continuously manage each category appropriately. High-risk vendors may require regular security scans or audits, while lower-risk vendors can be assessed annually. By the way, third-party risk management should not be “set-and-forget”; questionnaires and security audits should be done periodically and monitored in real-time.
Automating these tasks is often necessary since manually handling hundreds of vendors would overwhelm any security team. Practically, a mature program will use automation to scale audits, track remediation tasks, and generate risk dashboards. Solutions like ComplyScore® by Atlas Systems are designed specifically for these needs.
Following these steps creates a prudent TPRM program. You’ll know who your vendors are, understand their risk profiles, and have workflows in place to monitor and improve their security over time. The upside is the ability to catch issues early and respond quickly if a third-party incident occurs.
When evaluating a TPRM platform, the questions that actually separate vendors are:
Third-party cyber risk is an inevitable reality in today’s connected business environment and may seem daunting. From software providers to non-technical service partners, every external entity poses an inherent risk, a potential vulnerability. By understanding the different types of third-party risks, identifying your vendors, conducting thorough assessments, and implementing continuous monitoring, you can significantly reduce the odds of a vendor breach derailing your business. In today’s hyper-connected environment, managing third-party risk is not optional, it’s essential to protect your operations, data, and reputation.
Atlas Systems’ ComplyScore® is a complete third-party risk management solution tailored to your industry’s compliance needs that makes this process smarter, faster, and easier. With features like automated assessments, real-time monitoring, and centralized reporting, our platform simplifies risk management. Ready to take control of your third-party risk?
Explore how ComplyScore® can streamline your third-party risk management, reduce manual effort, and keep your business audit-ready at all times.
A third-party cyber risk assessment evaluates the security level of a vendor by analyzing their controls, systems, and processes. It typically involves setting risk criteria, categorizing vendors based on potential impact, and using tools to monitor their security hygiene over time.
An efficient evaluation follows the vendor lifecycle rather than a one-time questionnaire:
Beyond cyber-attacks, vendors can pose a strategic quarantine risk. A critical supplier might face a natural disaster, regulatory action, or sudden insolvency that disrupts your operations even without a security breach.
You should enquire about consistency, accountability, metrics, and integration of processes into enterprise frameworks. Some sample questions would be:
Industry experts point out that continuous monitoring and lifecycle management are crucial. Simply conducting initial assessments won’t be effective enough. TPRM solutions like Complyscore continuously monitor vendors to ensure the best security for your data.