ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management. 



Continuous Compliance Automation Software That Keeps You Audit-Ready
Verify your cloud controls, internal data flows, and breach readiness continuously, so your evidence is always current when a regulator, auditor, or customer asks for it.
<30 Days
Audit readiness
70-80%
Less manual effort
40-60%
Lower assessment costs
Trusted partner to market-leading brands


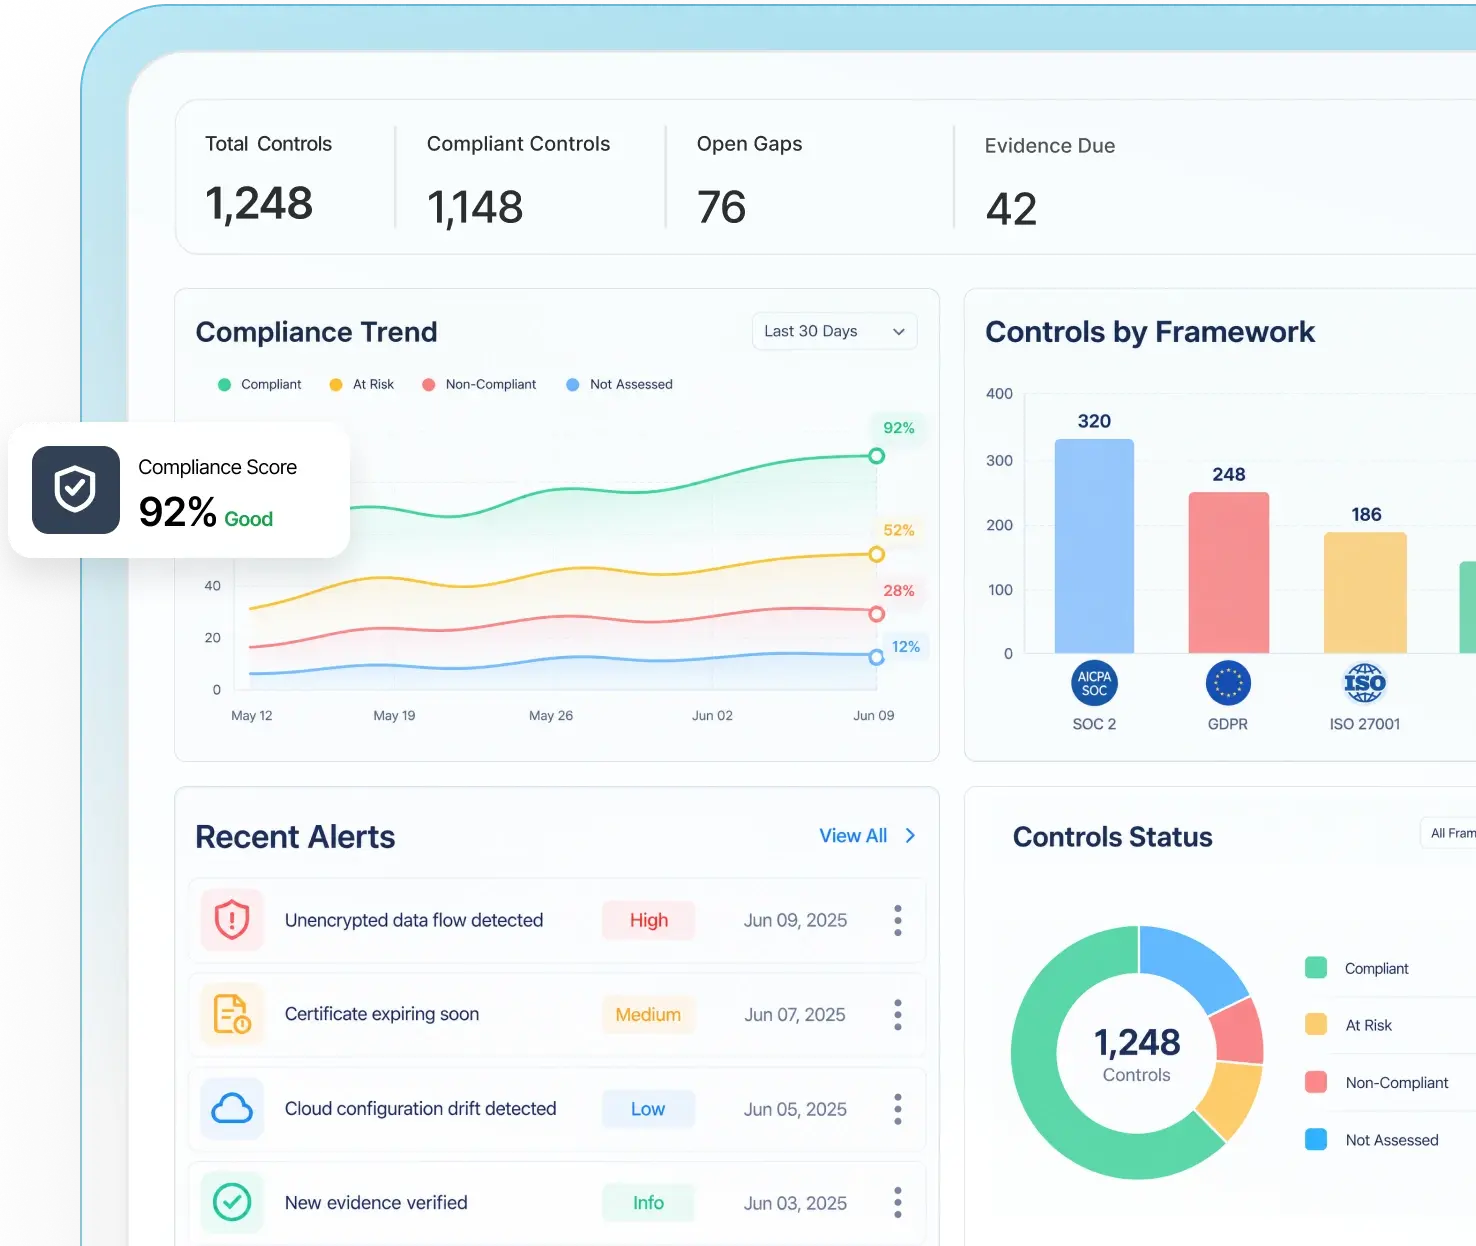
How ComplyScore® Keeps You Audit-Ready, Always

Continuous control verification

Chat and voice access
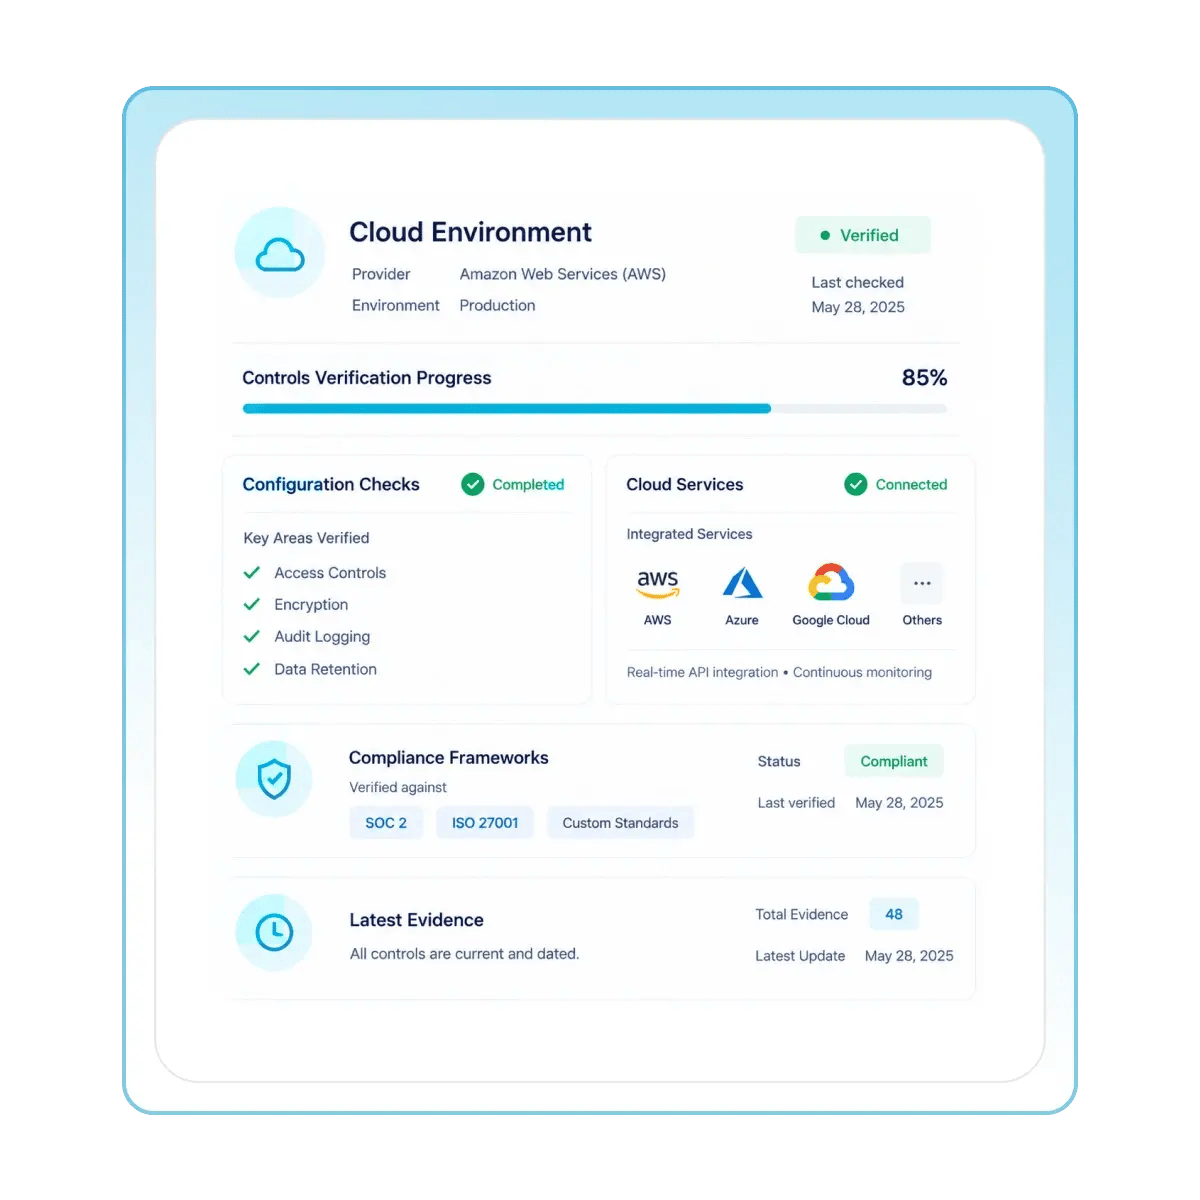
Verify Your Cloud Environment
Policy documents describe intended configurations. ComplyScore® verifies what's actually deployed, checking access controls, encryption, audit logging, and retention against SOC 2, ISO 27001, or your own standards. Evidence stays current and dated, ready for examination anytime.

70-80% reduction in manual evidence gathering.

Data flow mapping

Consent and notice verification
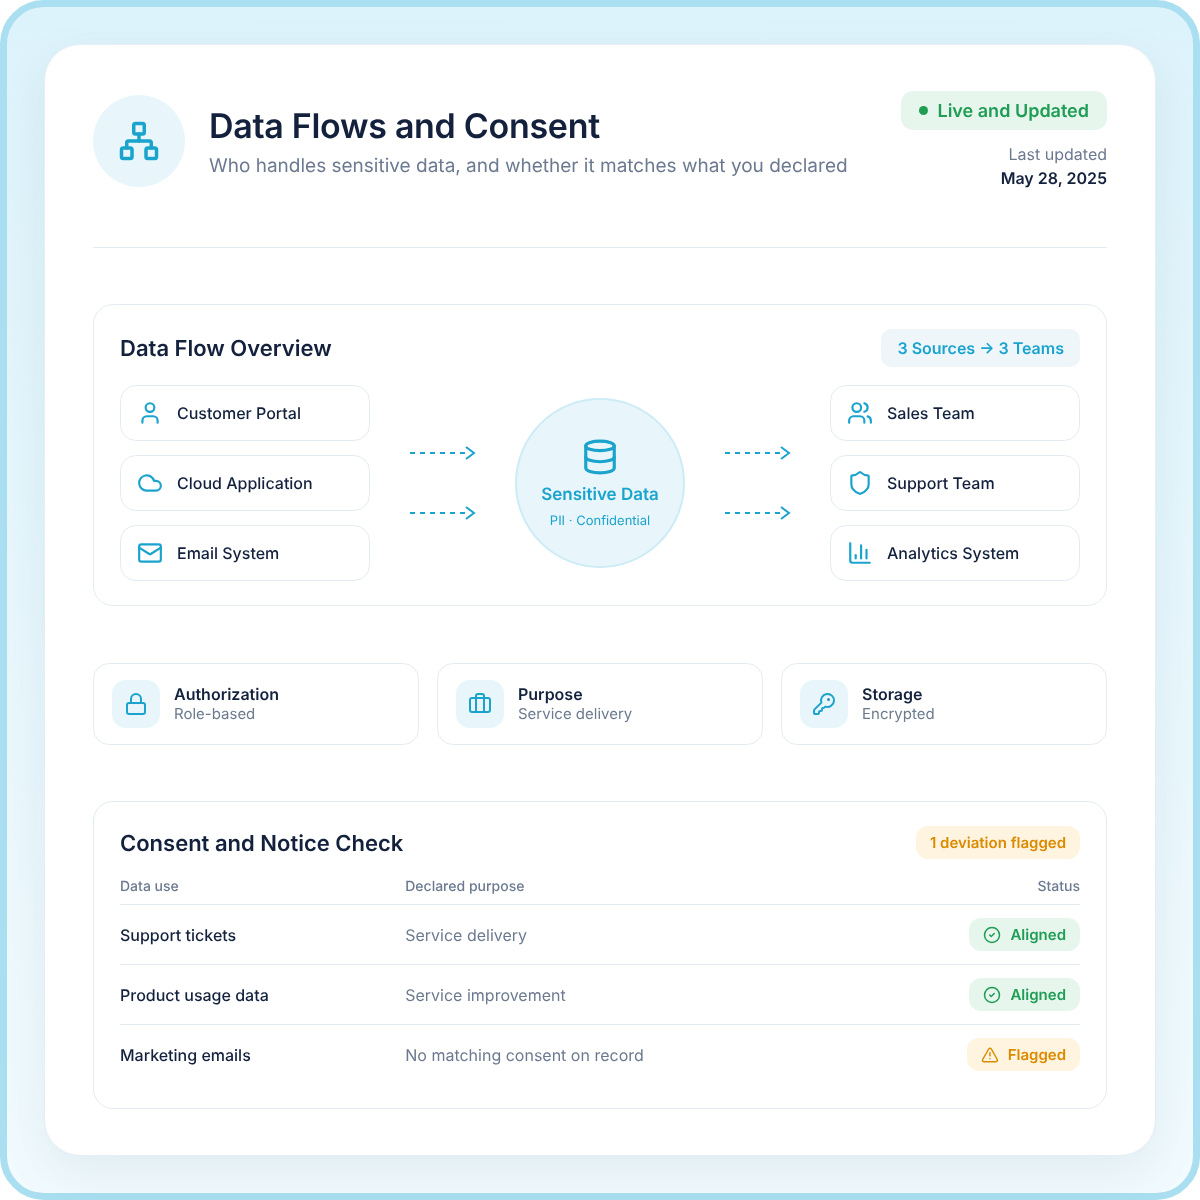
Keep Data Flows and Consent Accurate
ComplyScore® keeps a living record of which teams handle sensitive data, under what authorization, and why. It checks each use against your consent and notice records and flags drift before an examination does.

Every sensitive data flow carries an owner, an authorization, and a declared purpose.

Owned remediation

Auditor workspace
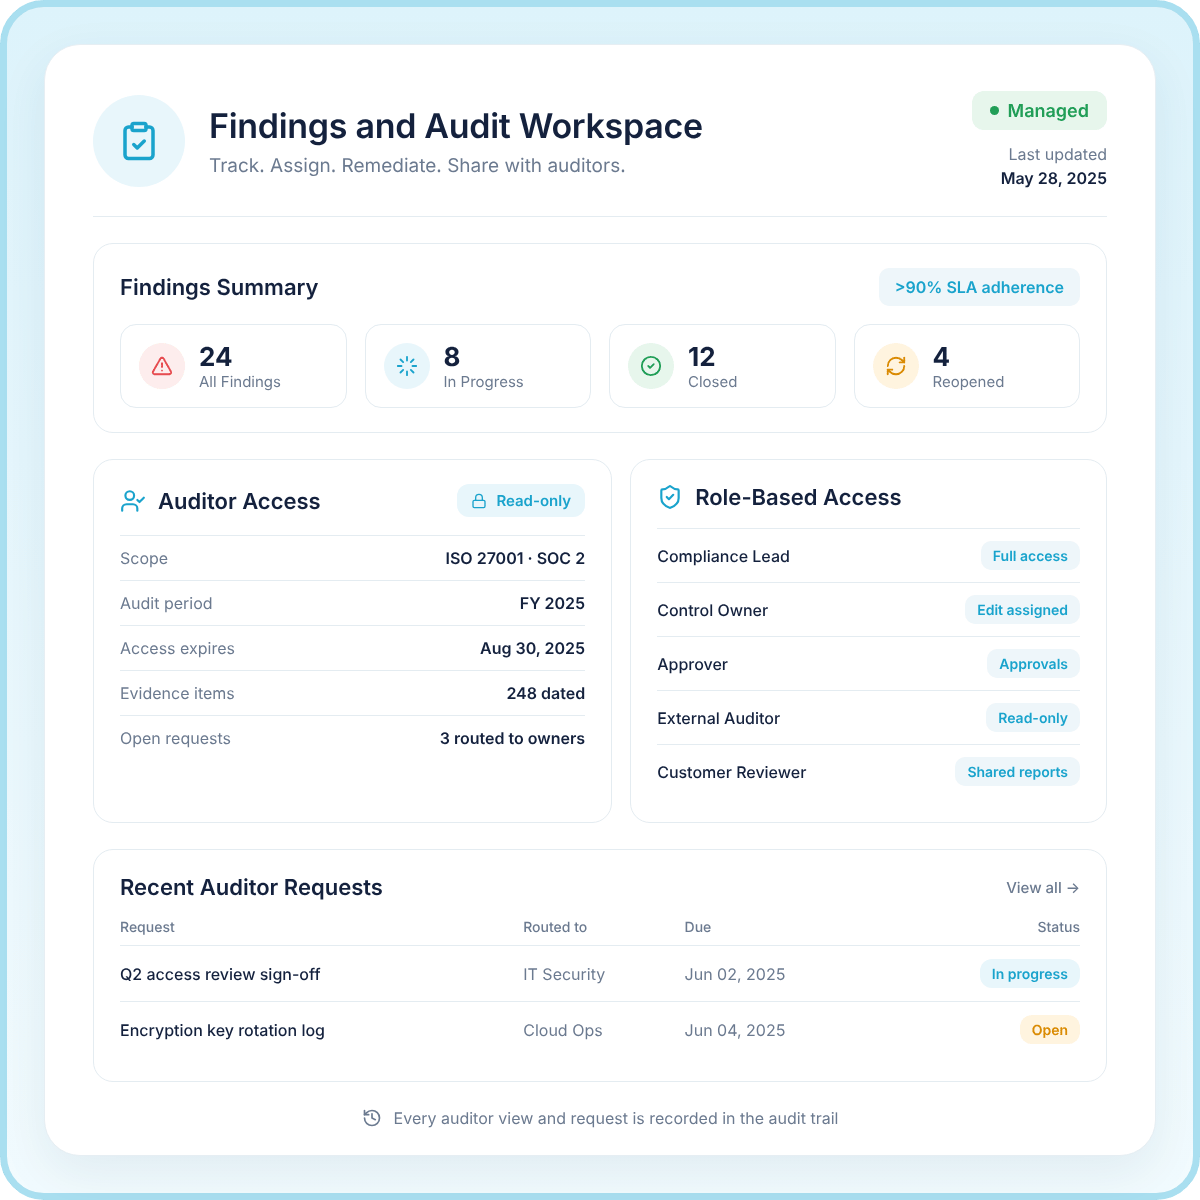
Close Findings and Give Auditors One Place to Review
Every finding routes to an owner with a deadline and automatic escalation. Auditors get a separate, read-only login to review controls, dated evidence, and remediation history in one place, with role-based access for everyone else.
>90% SLA adherence on findings tracked through ComplyScore® governed workflows.

Breach readiness documentation

Tested response procedures
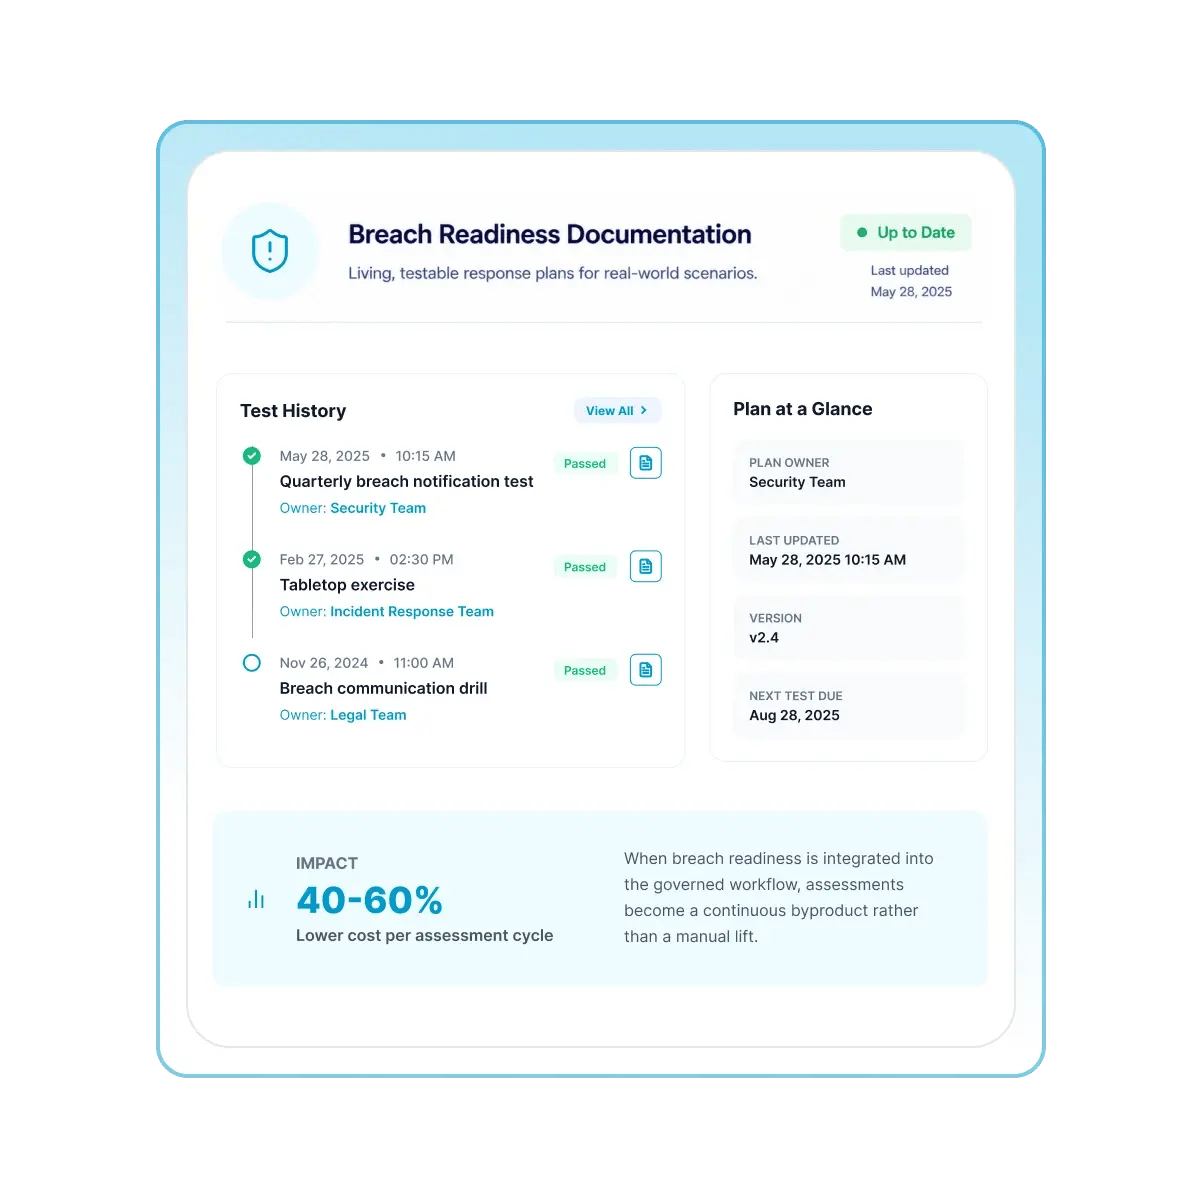
Document Readiness
A response plan only becomes a compliance asset once it's tested. ComplyScore® keeps breach notification procedures as living, testable documentation, timestamped with assigned owners and proof of execution. That gap between intent and demonstrated capability is where programs fail under pressure.

40-60% lower cost per assessment cycle when breach readiness is integrated into the governed workflow.
AI evidence review
30+ frameworks
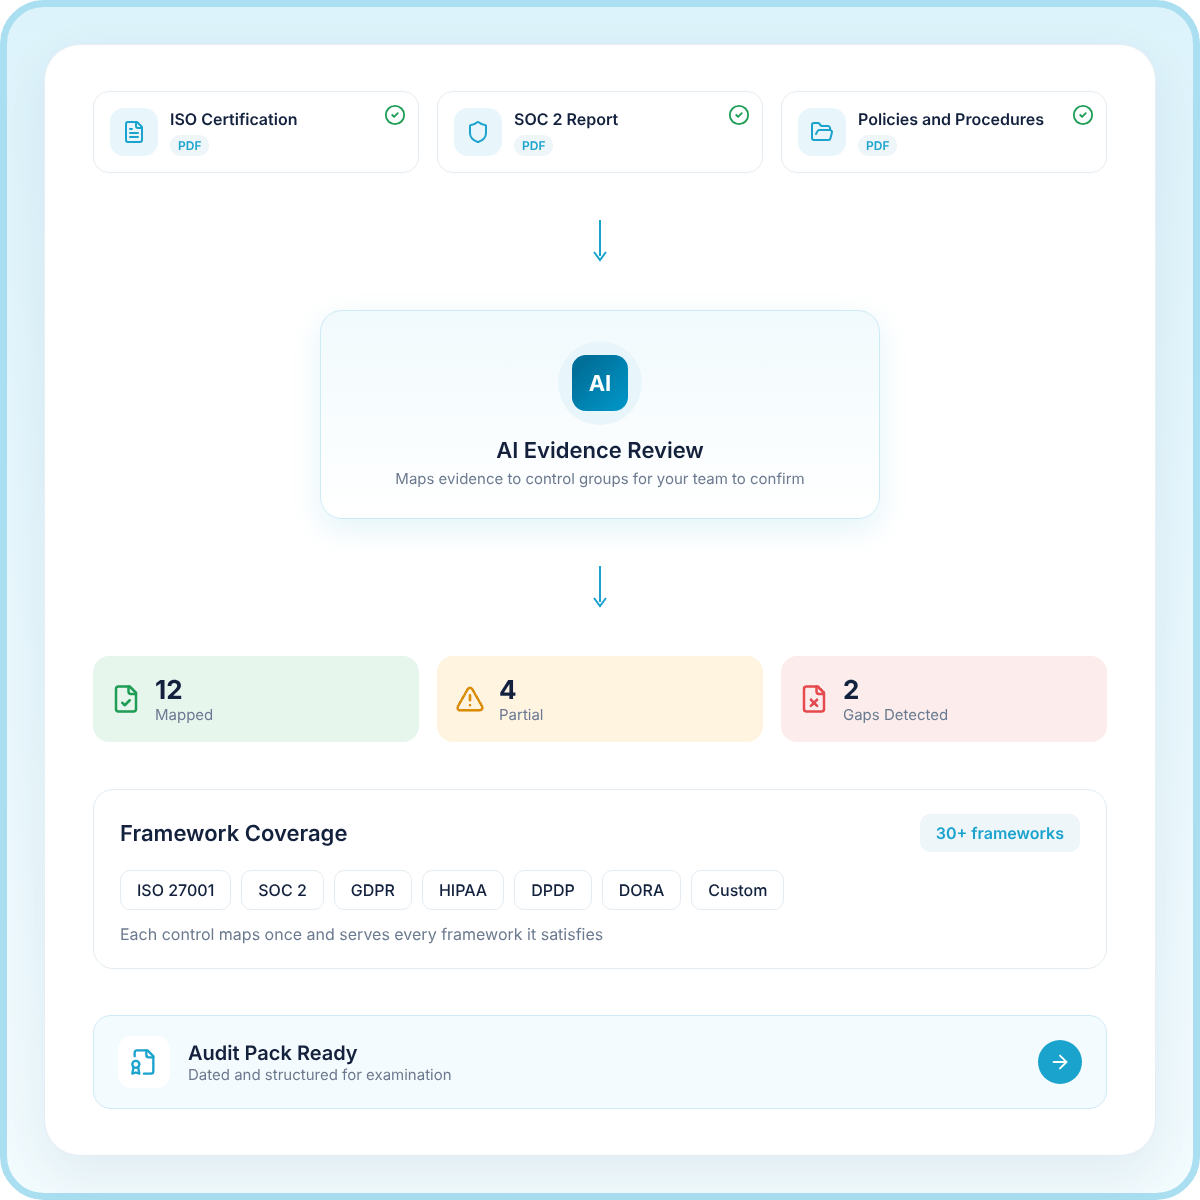
AI Does the First Pass, You Make the Call
ComplyScore®’s AI scans uploaded evidence like ISO and SOC 2 certifications, maps it to the right control groups, and flags gaps for you to confirm. Start from 30+ frameworks, including GDPR, HIPAA, DPDP, and DORA, or your own standards, and map each control once. Ask about anything flagged in chat or by voice.
<30 days to a current, evidence-based audit pack.
What You Can Do With ComplyScore® Self-Assessment


Proven Results Across Industries
Trusted partner to market-leading brands


Atlas far exceeds our requirements...
One of the key differentiators between Atlas and other governance, risk and compliance and 3rd party risk management tools is the ease of use of the Atlas solutions. Also from a total cost of ownership perspective, Atlas far exceeds those requirements in terms of being very cost efficient in delivering all this.
ComplyScore is highly responsive and adaptable
ComplyScore is highly responsive and adaptable to our evolving processes and requirements, proving to be a trusted partner at every step. Their security analysts were knowledgeable, flexible, and delivered exceptional services that consistently exceeded our expectations.
My experience has been largely positive
I have been using ComplyScore for several months and my experience has been largely positive. The platform provides comprehensive solutions for compliance management and streamlines our operations efficiently.
As our business grew across geographies
As our business grew across geographies, we needed a more scalable approach to vendor lifecycle management. ComplyScore® provides the governance, flexibility & visibility to support our global operations while strengthening compliance and risk management across our vendor ecosystem.
Trusted by Industry Leaders for TPRM and Self Assessments

Representative Vendor | Listed in 2025 Market Guide for TPRM Technology Solutions

Active partner member of the Third Party Risk Association
