


Third-Party Risk Management
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management. 
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management.
Automate onboarding, evidence review, and monitoring across every vendor and third-party relationship, while GDPR, DORA, and NIS2 stay mapped in the background.
Risk assessments
Vendor coverage
Lower assessment costs



Auto-enriched profiles

Pre-filled questionnaires
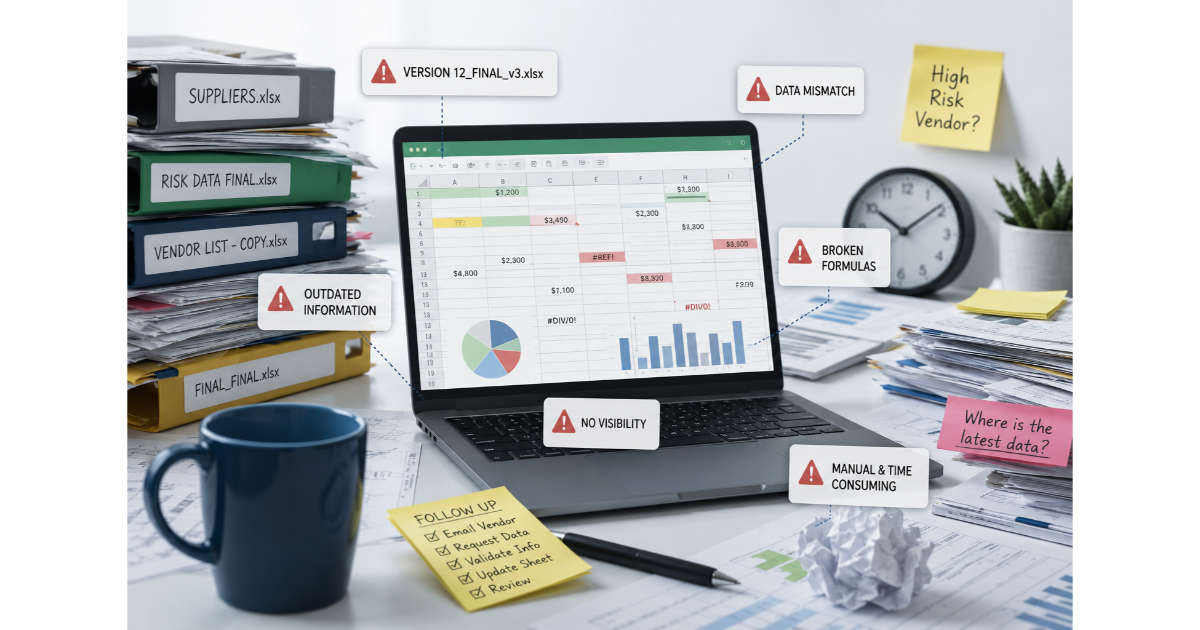
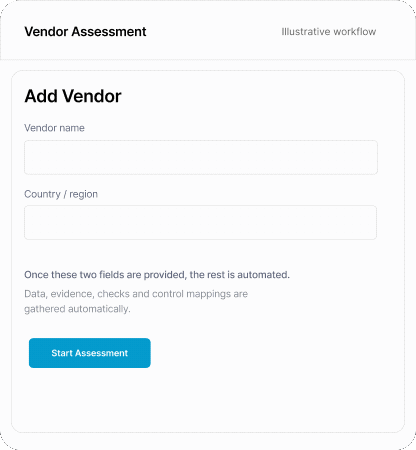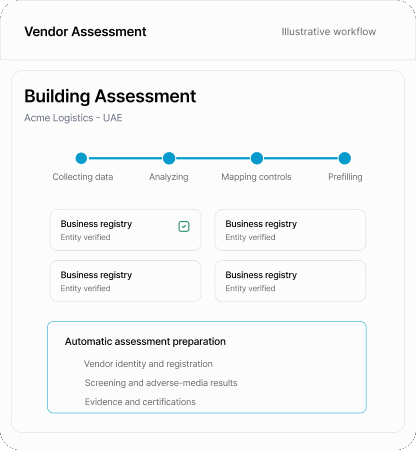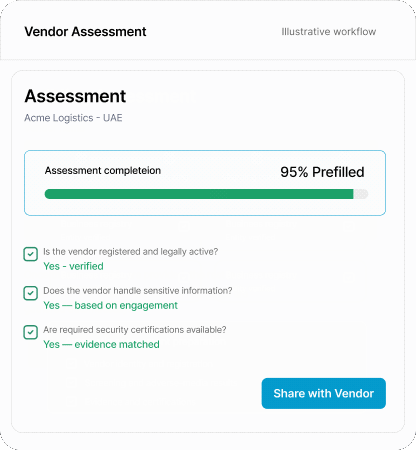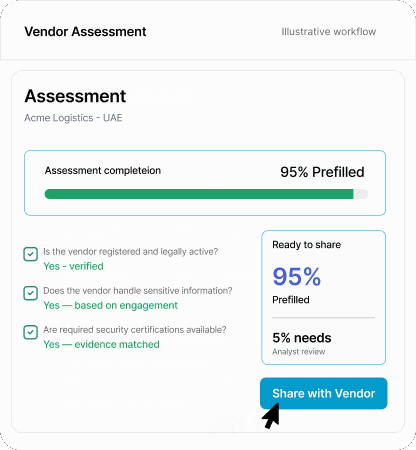
With zero-touch assessments, vendor profiles arrive pre-populated from registries and certifications. Questionnaires start pre-filled, so your team reviews instead of chasing blank forms.

<10 Days average vendor onboarding time, down from 45 to 60 days.

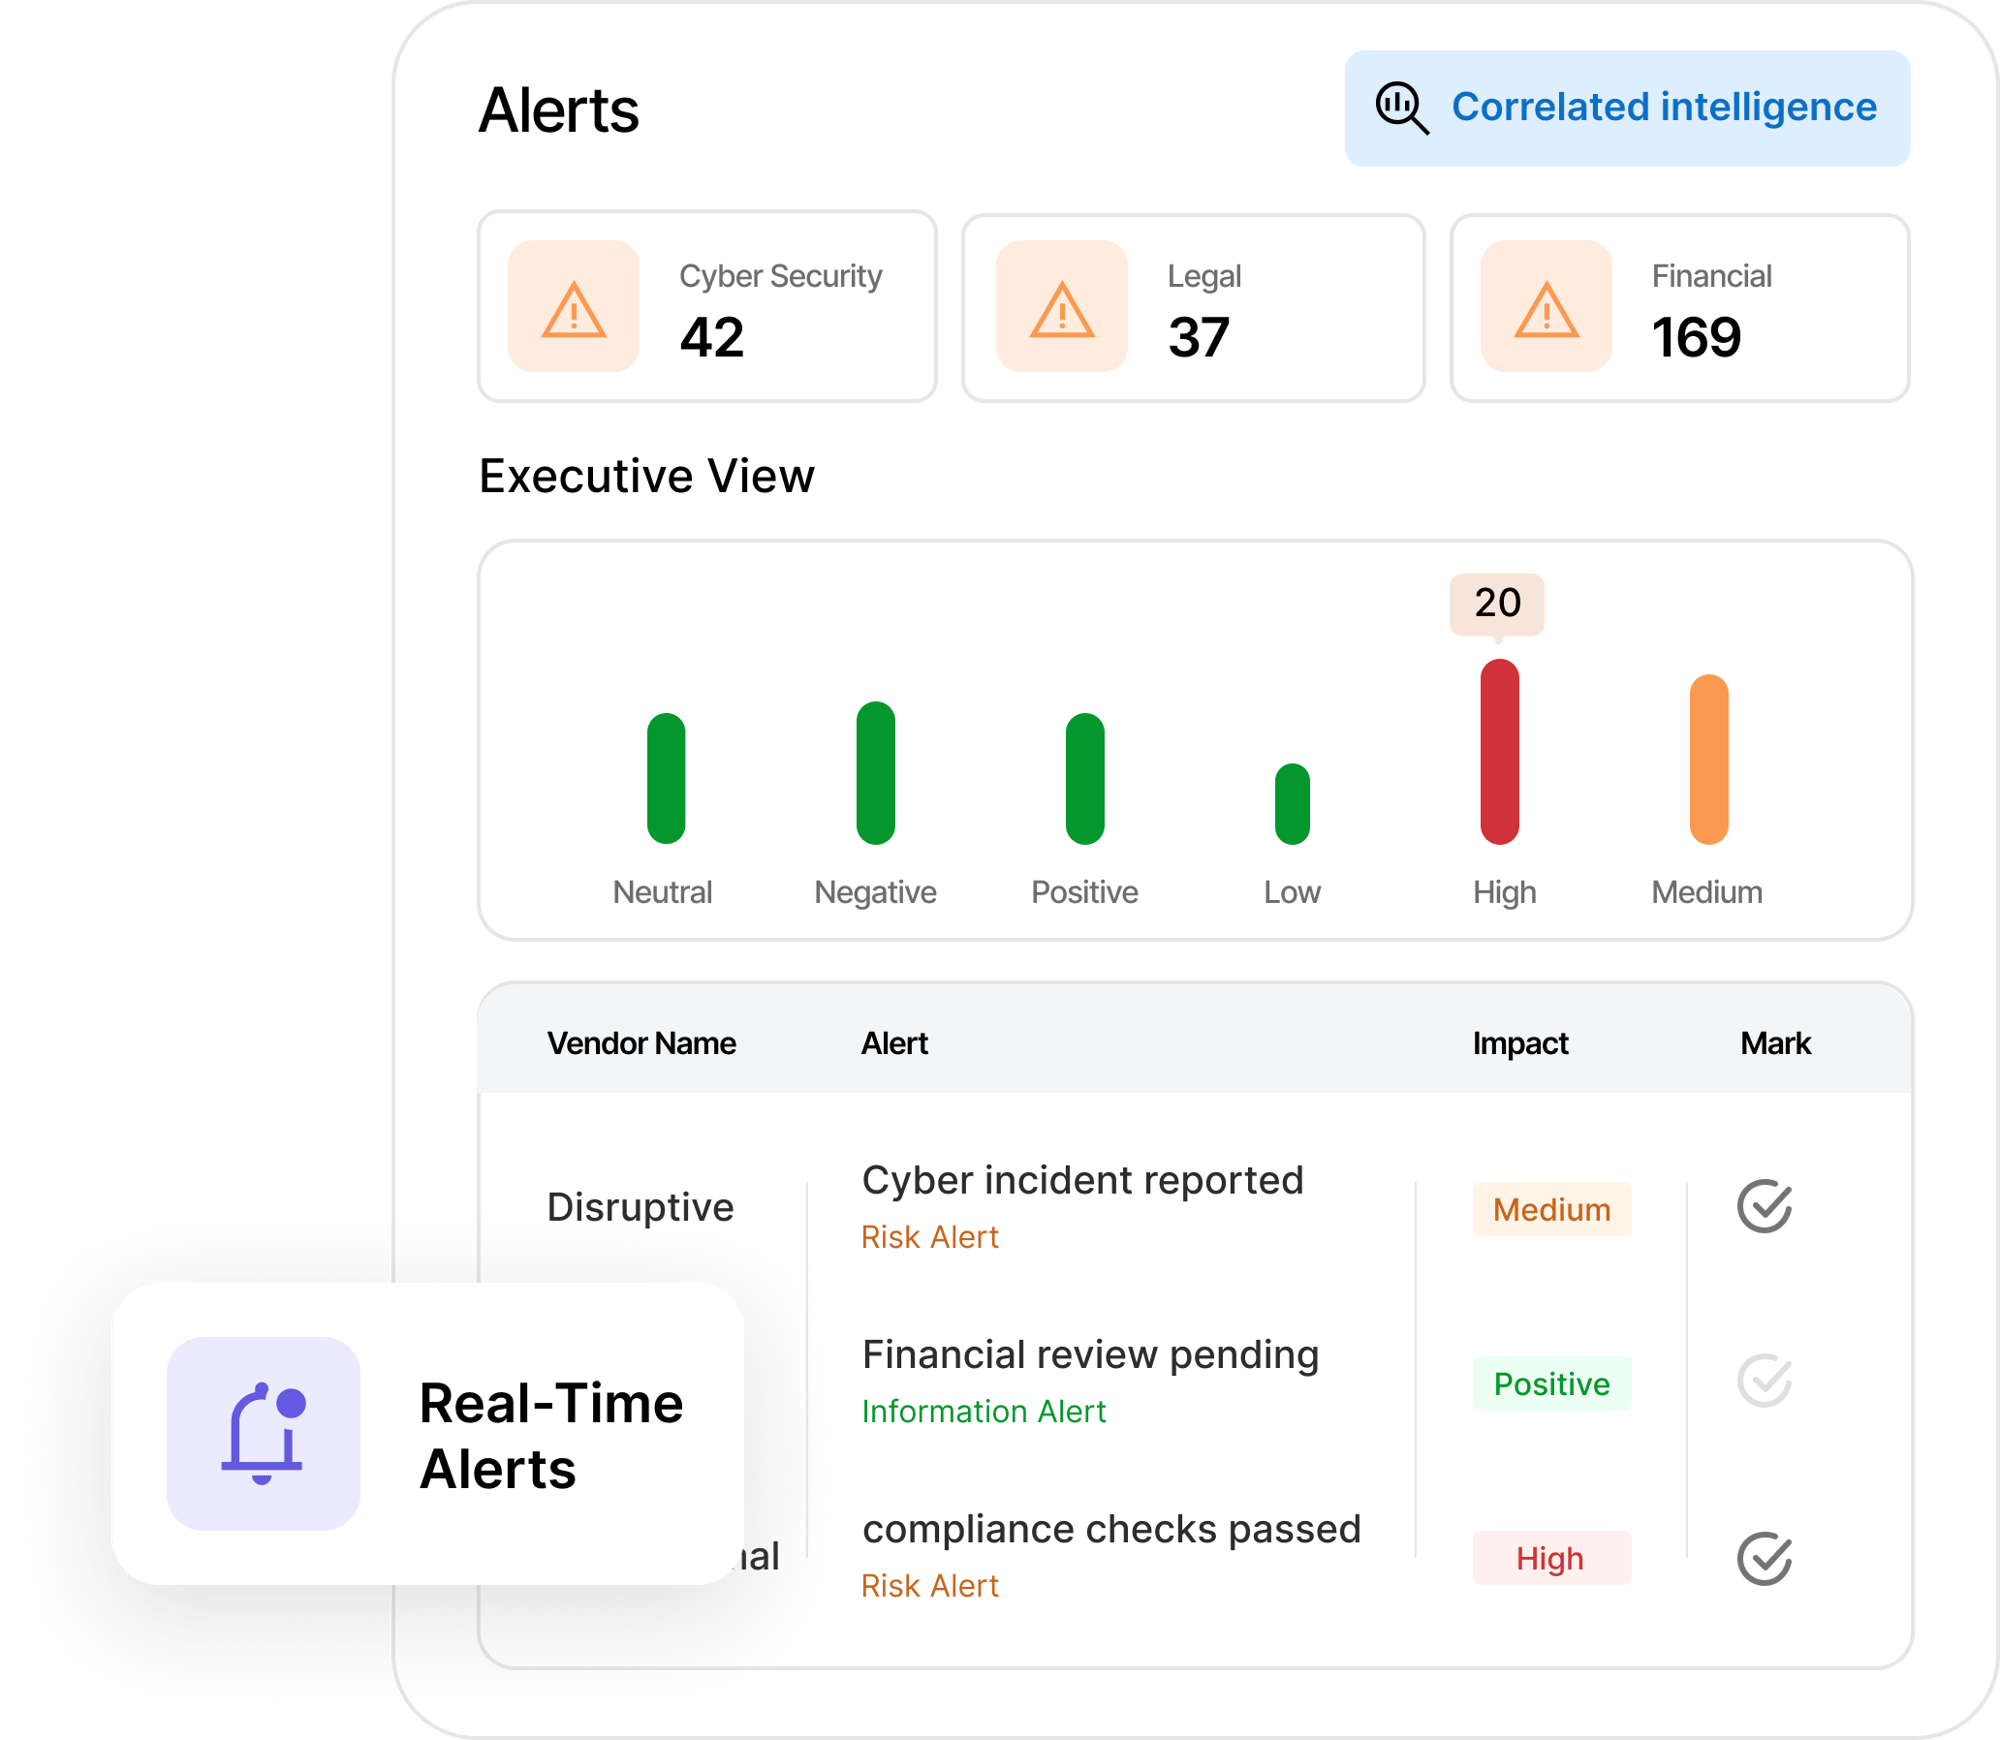
Real-time alerts

Correlated intelligence
ComplyScore® pulls cyber, financial, and operational signals and routes material changes as owned tasks with SLAs. DORA’s register of information and NIS2’s incident timelines both call for this kind of standing visibility.

Teams reach over 90% SLA adherence vs. an industry average of 50-65%.

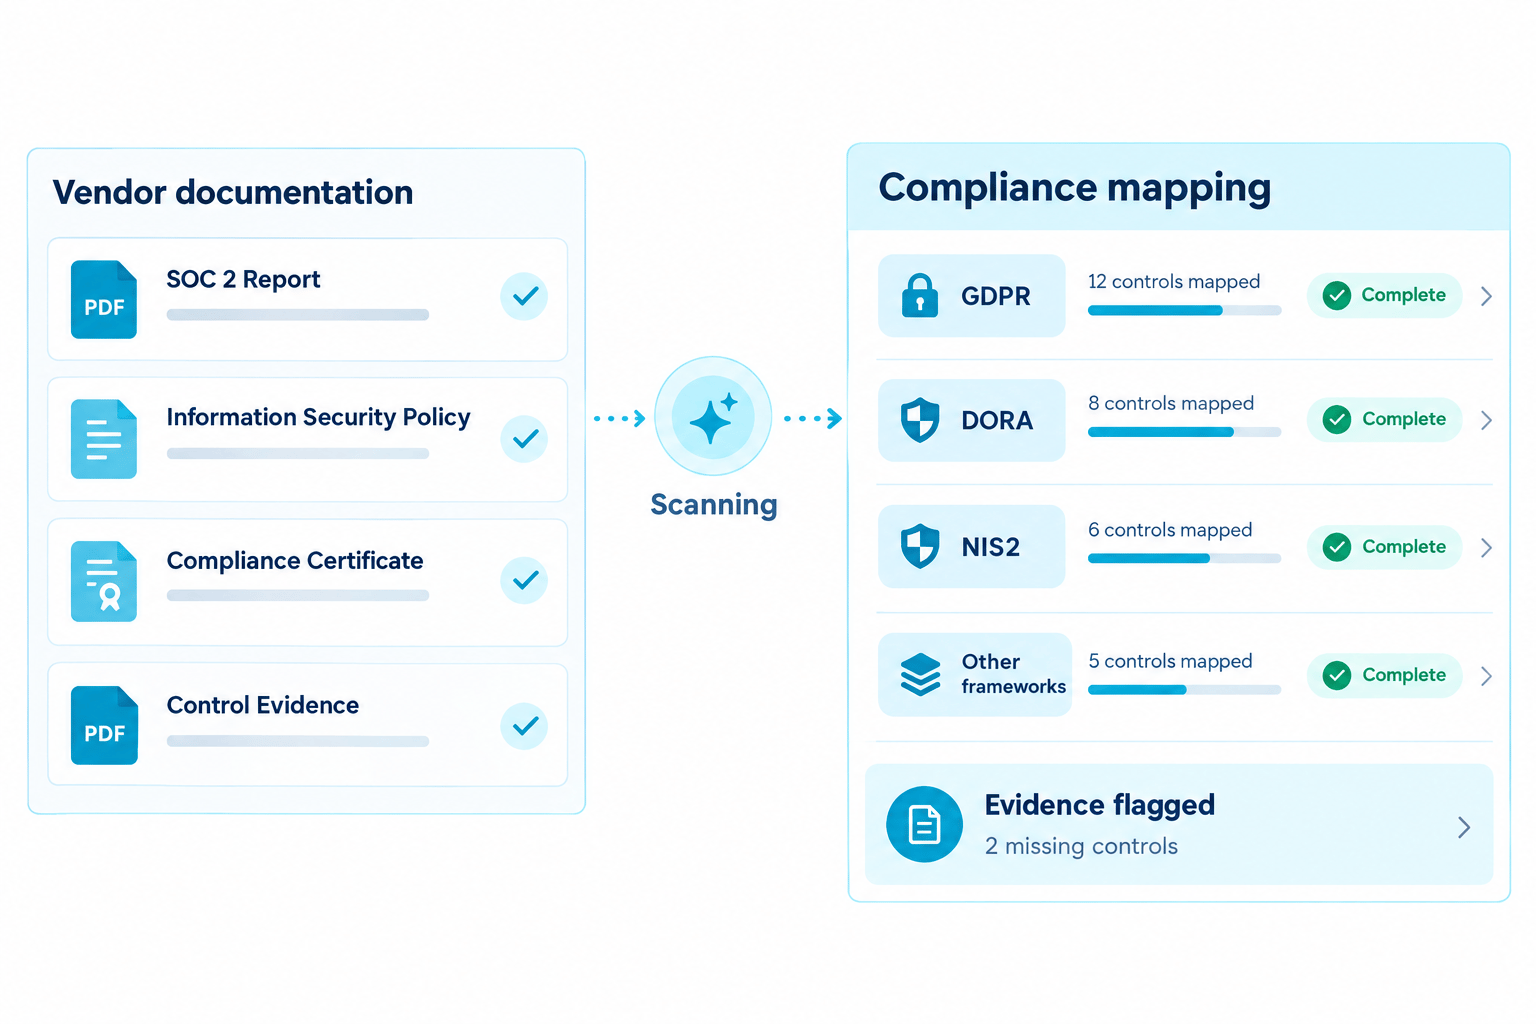
AI document intelligence

Framework-aware scoring
ComplyScore® scans SOC 2 reports, policies, and certificates to flag missing controls and check response consistency across vendors. Evidence maps to GDPR, DORA, NIS2, and other frameworks during the assessment itself.
Assessments complete in under 10 days vs. an industry average of 30-45 days.

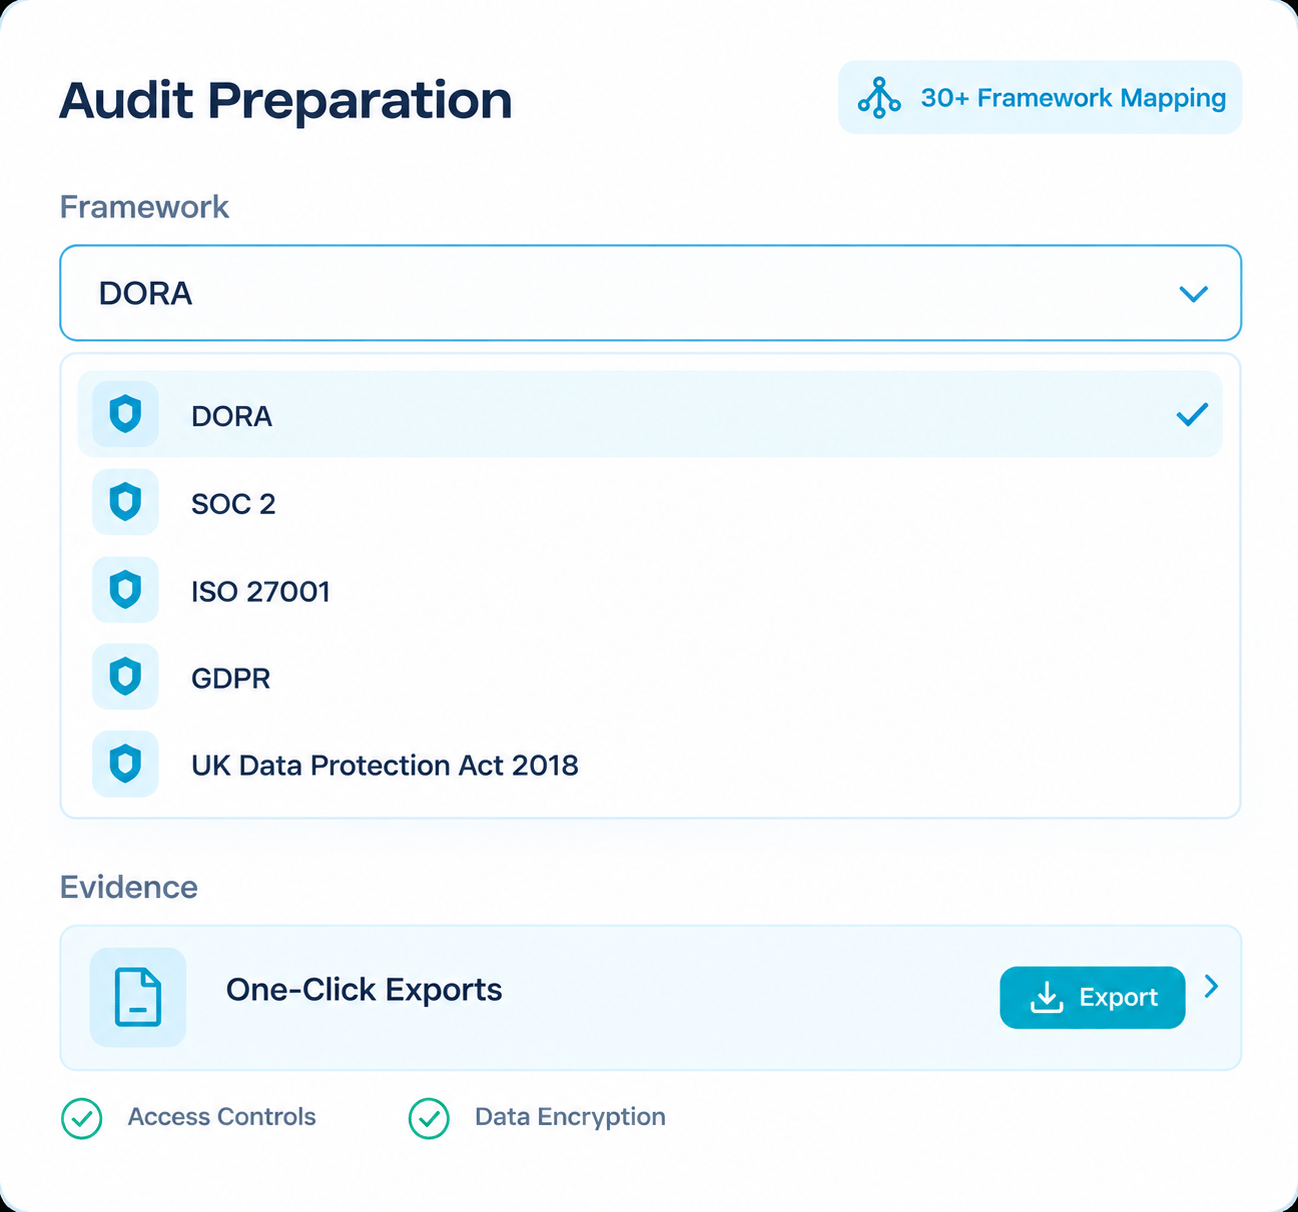
30+ framework mappings

One-click exports
Controls map to GDPR, DORA, NIS2, and the UK Data Protection Act 2018 as assessments happen. Evidence packs export in seconds, already aligned to the framework an auditor asks for.

Audit preparation effort drops by up to 60% through automated mapping.

Right-size assessments based on vendor criticality and data exposure.

Query vendor risk data in plain language instead of building dashboards. Headless TPRM gives instant answers, no separate interface required.

Give leadership live KPIs with drill-through access to evidence.

Govern vendors and other third parties from contract signature through offboarding.


One of the key differentiators between Atlas and other governance, risk and compliance and 3rd party risk management tools is the ease of use of the Atlas solutions. Also from a total cost of ownership perspective, Atlas far exceeds those requirements in terms of being very cost efficient in delivering all this.
ComplyScore is highly responsive and adaptable to our evolving processes and requirements, proving to be a trusted partner at every step. Their security analysts were knowledgeable, flexible, and delivered exceptional services that consistently exceeded our expectations.
I have been using ComplyScore for several months and my experience has been largely positive. The platform provides comprehensive solutions for compliance management and streamlines our operations efficiently.
we needed a more scalable approach to vendor lifecycle management. ComplyScore® provides the governance, flexibility & visibility to support our global operations while strengthening compliance and risk management across our vendor ecosystem.