Why Securing Legacy Medical Devices Is Critical for Healthcare Cybersecurity

1 min read | Last Updated: 30 Jul, 2026
Hospitals rely on legacy medical devices that remain critical for patient care but were never designed for today’s cyber threat landscape. These outdated systems create blind spots that attackers can exploit, putting both patient safety and hospital operations at risk.
That’s where risk-based security strategies come in. In his interview with 24×7, Kaarthick Subramanian, Chief Customer Experience Officer at Atlas Systems, explains why isolating vulnerable devices, monitoring them closely, and working with IT and vendors is essential to reducing exposure without disrupting care.
Related Reading
Third-Party Risk Management
AI-Driven Due Diligence: Stop Assessing Vendors, Start Understanding Them
Nasir R
|
Jun 30, 2026
Read the blog
→
Third-Party Risk Management
What Integrated Risk Management Systems Miss About Third-Party Risk
Nasir R
|
Jun 30, 2026
Read the blog
→
Third-Party Risk Management
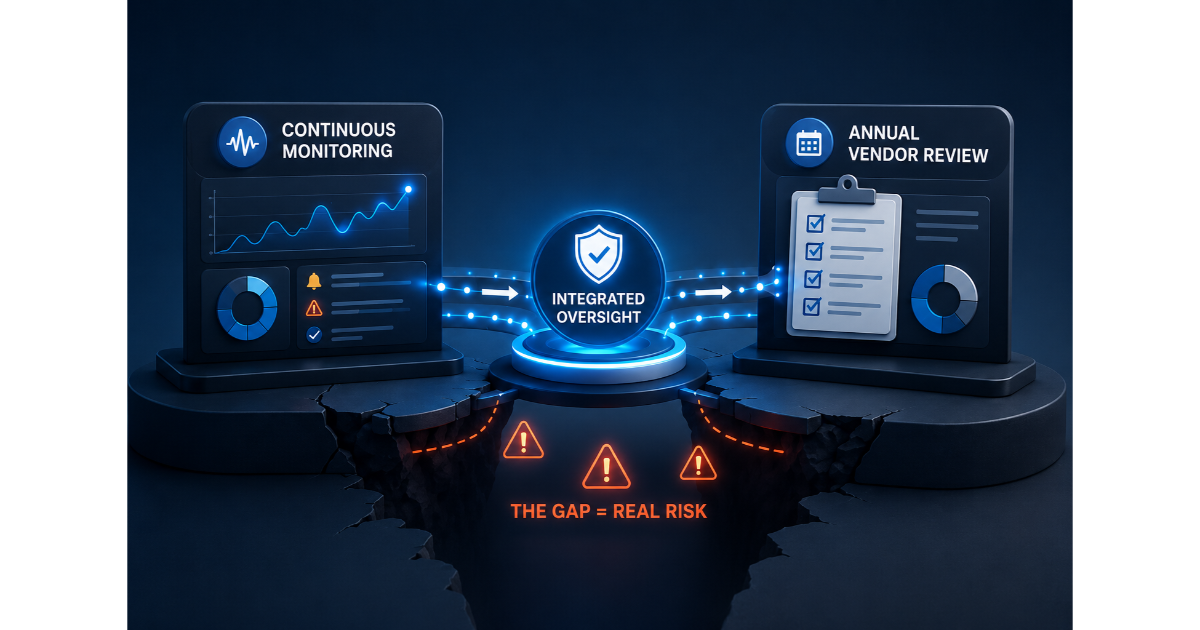
Continuous Monitoring vs. Annual Vendor Review: Why the Real Risk Lives in the Gap Between Them
Nasir R
|
Jun 10, 2026
Read the blog
→
Third-Party Risk Management
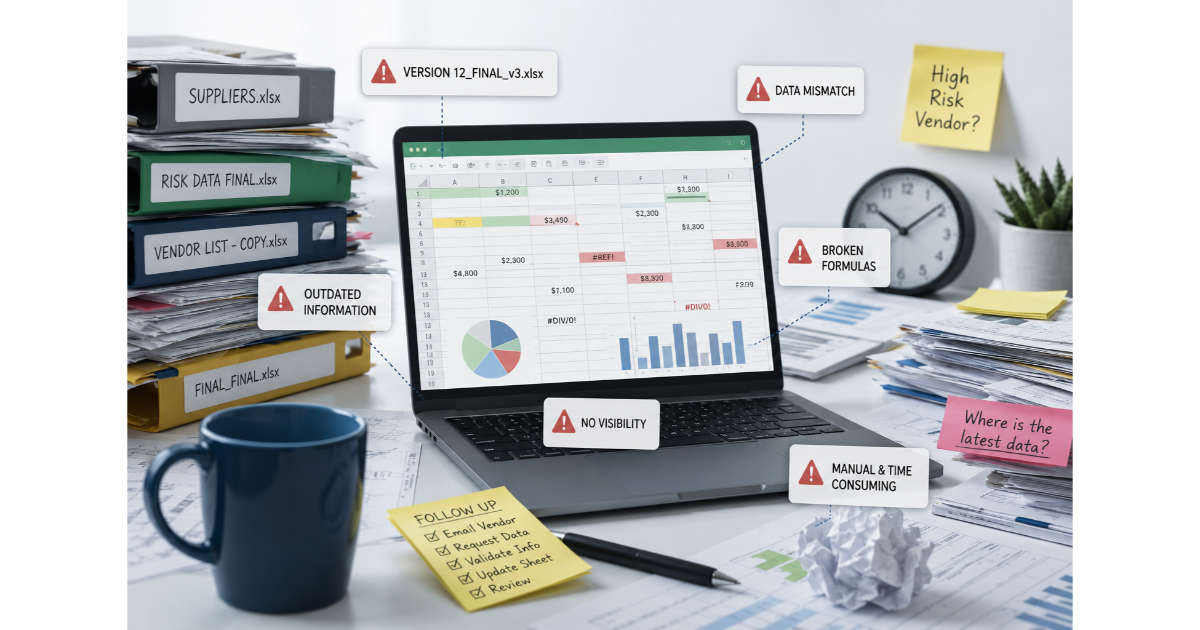
Why Spreadsheets Fail in Third Party Risk Management
Nasir R
|
Jun 10, 2026
Read the blog
→
Third-Party Risk Management
The 7 stages of a TPRM Process, What Goes Wrong, and How to Fix It
Nasir R
|
Apr 30, 2026
Read the blog
→